Real-time heartbeat & revoke
Products phone home. Revoke once — every instance stops within one heartbeat cycle. Grace period for offline clients.
Machine-locked licensing · Remote kill-switch · Air-gapped ready — OT SIEM/SOAR in pipeline.
Free trialAxix Hawk
Security
Cryptographic licensing, hardened runtimes, runtime detection, and tenant isolation — designed for hostile client environments.
Each layer independent; all required.
Products phone home. Revoke once — every instance stops within one heartbeat cycle. Grace period for offline clients.
No shell, no package manager, syscall whitelist. Images signed with cosign; unsigned containers refuse to start.
SSO for end users. Tokens bound to machineId — valid JWT on the wrong hardware is rejected.
Signed blobs with org, product, tier, features, expiry. Embedded public key — no server needed to verify offline.
SHA-256 of stable host signals. Licenses cannot be copied to another machine without re-issuance.
License blobs signed so clients verify offline with an embedded public key.
Key material encrypted at rest in the Hawk control plane.
Lifecycle deliveries signed so receivers can reject forged events.
Stable host signals hashed into machine_id for binding.
RUNTIME HARDENING
No shell to strip licensing. Unsigned images refuse to start. Runtime rules catch shell-in-container, ptrace, and license exfiltration.
SSO boundaries per vendor tenant — roles on every API route.
Row-level security — zero cross-tenant leakage by design.
Valid tokens on the wrong hardware are rejected.
AUDIT
Every generate, revoke, deploy, heartbeat anomaly, and Falco alert lands in an append-only log — SOC 2-ready evidence for reviews.
Honest scope — not rubber-stamp claims.
Audit trails and access controls designed for readiness programs.
license_id, machine_id, versions — no PII by design.
Via OT SIEM/SOAR pipeline — labeled clearly as roadmap.
Core licensing + Falco today. OT SIEM/SOAR in development.
| Capability | Status |
|---|---|
| Licensing lifecycle | Live |
| Agent + SDKs | Live |
| Falco detection | Live |
| Audit + webhooks | Live |
| OT SIEM | Pipeline |
| OT SOAR | Pipeline |
| Advanced ICS protocol parsers | Pipeline |
| Full OT playbook library | Pipeline |
Hardware fingerprints and signatures stop casual license sharing.
Reduce the attack surface of what you ship to customer sites.
Show generate, revoke, and anomaly events when security asks.
Start free and prove bind failure and revoke timing to your reviewers.
Yes — license generate, revoke, deploy, and anomaly events land in an append-only trail suitable for security reviews.
We will map layers to your threat model and deployment modes.
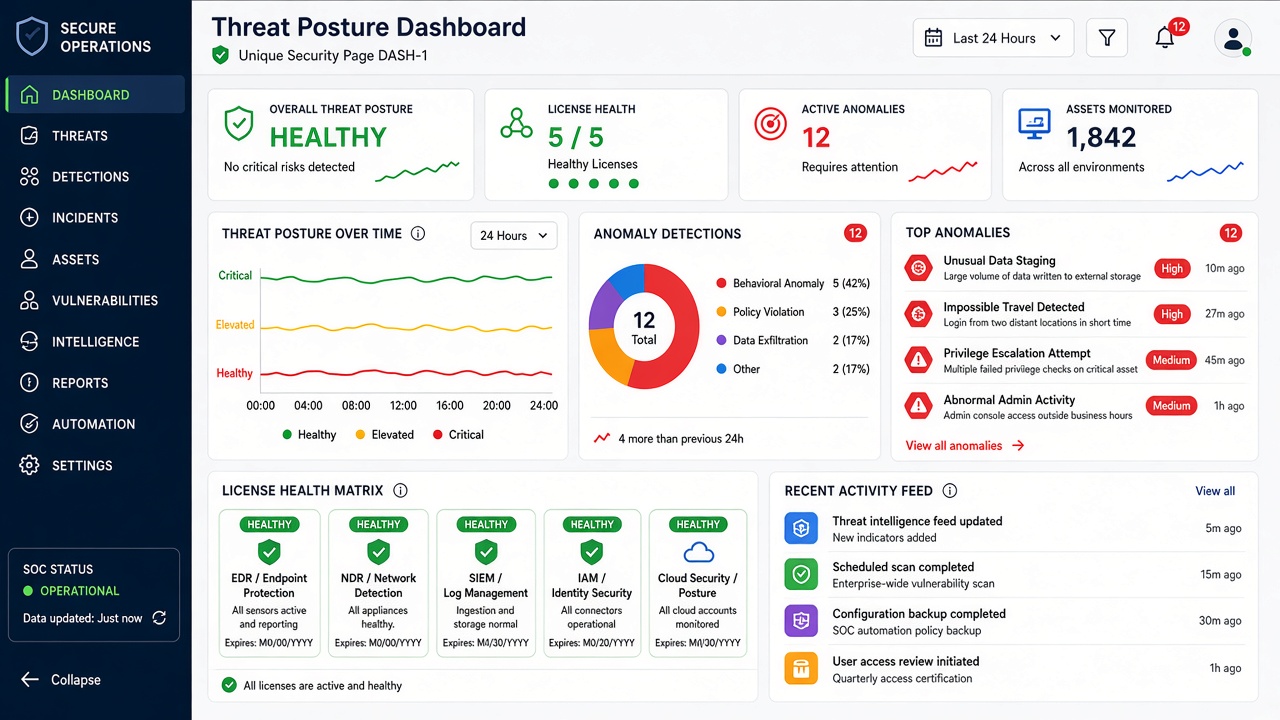
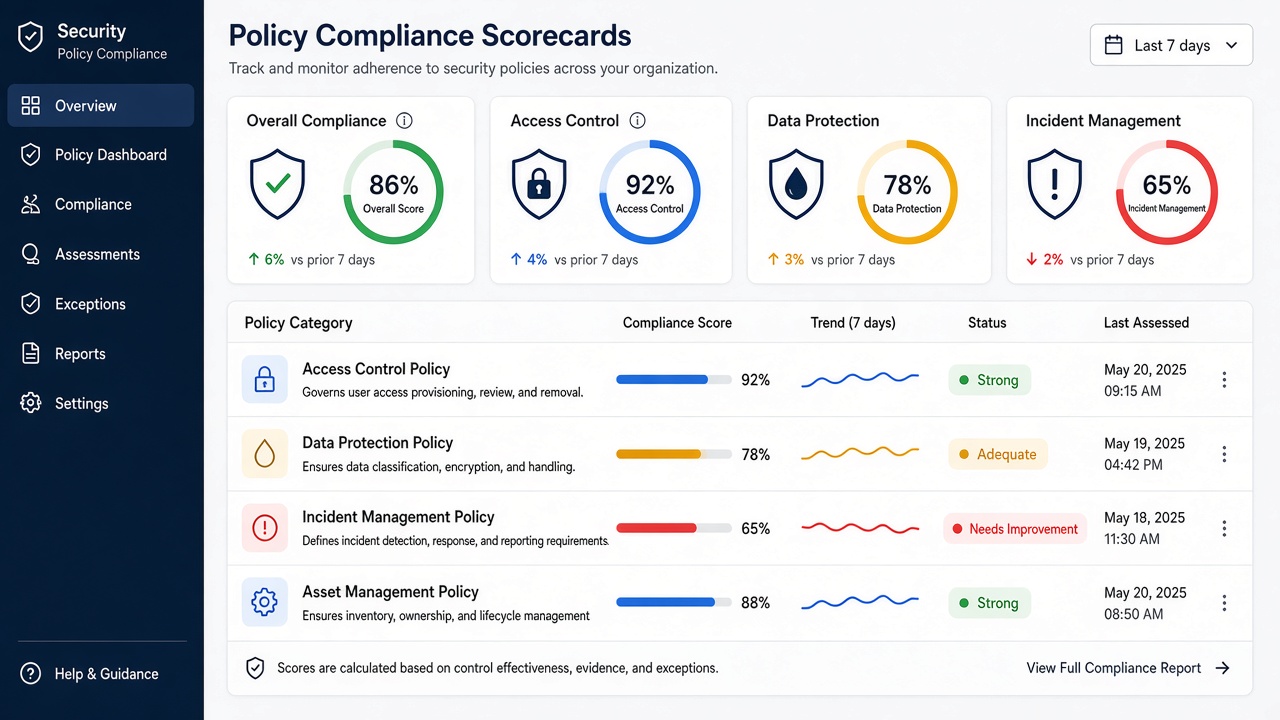
Three console views and three real-world moments for this page — each with a full caption.
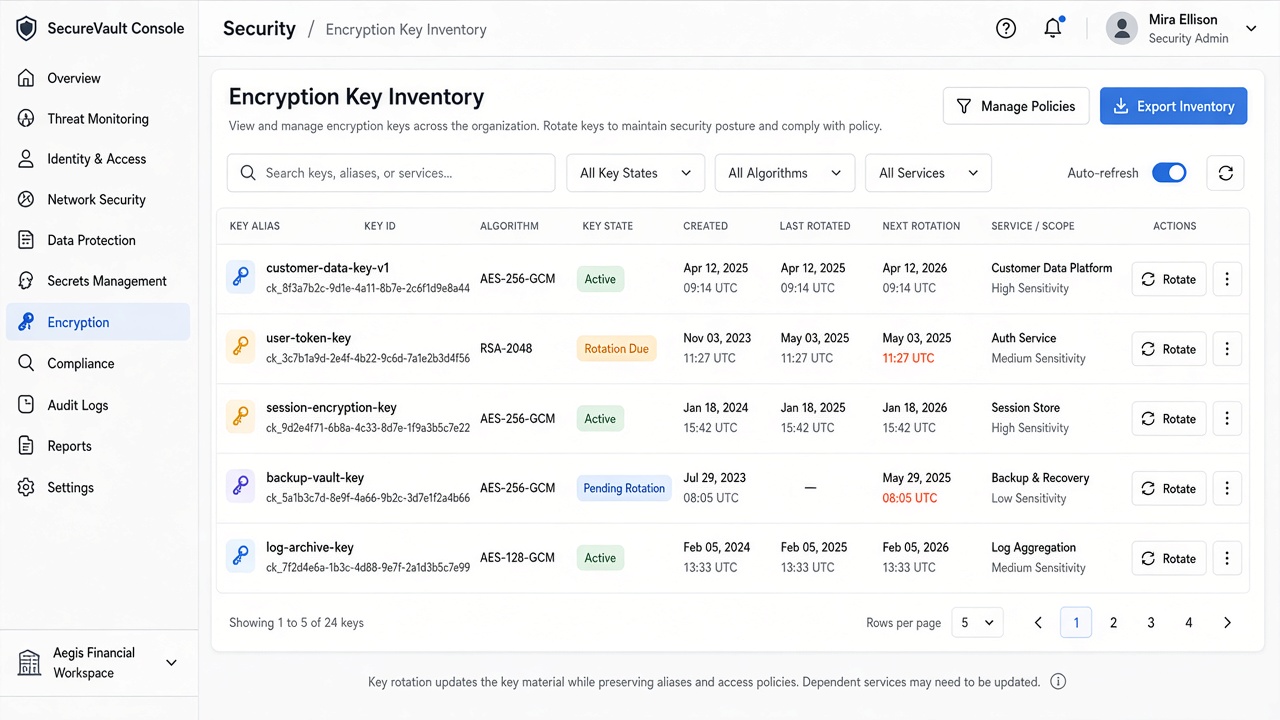
Console view for Security: license inventory, bind status, and org filters in one workspace. Operators scan Active versus Revoked rows, confirm machine fingerprints, and jump into a client without leaving the grid. Search and column controls keep large fleets readable. This frame is unique to this page so the visual story matches the URL you opened.
Second dashboard for Security: heartbeat health, revoke timing, and anomaly hints sit side by side. Use it to brief security on what “one heartbeat” looks like before a PoC. Charts stay light-themed with navy accents for Axix Hawk. Nothing here is reused from another marketing route.
Third console moment for Security: deployment analytics and seat pressure across client orgs. Leaders see where licenses concentrate and where renewals are due. Export-friendly layout supports review packs. Paired with this page’s copy so buyers never see a generic stock screen.
People moment one for Security: practitioners reviewing Hawk controls in a real workspace. The scene grounds licensing talk in day-to-day operations instead of abstract icons. Lighting and wardrobe stay professional and brand-safe. Captured specifically for this page’s narrative so visitors never confuse it with another product route.
People moment two for Security: collaboration around ship-or-hold decisions after a revoke drill. Teams align on evidence — bind failure, kill-switch timing, audit export — before a customer demo. Atmosphere matches Axix Hawk’s light navy product language. Unique to this route’s gallery.
People moment three for Security: field or office context for how this capability lands with buyers. Use it to show human stakes behind machine-locked software. Composition avoids logos and keeps faces secondary to the work. Written and imaged only for the Security page experience.